What if someone can reach on your FileMaker Server without a username or password?
The recent attacks on FileMaker servers have made that question urgent for our community.
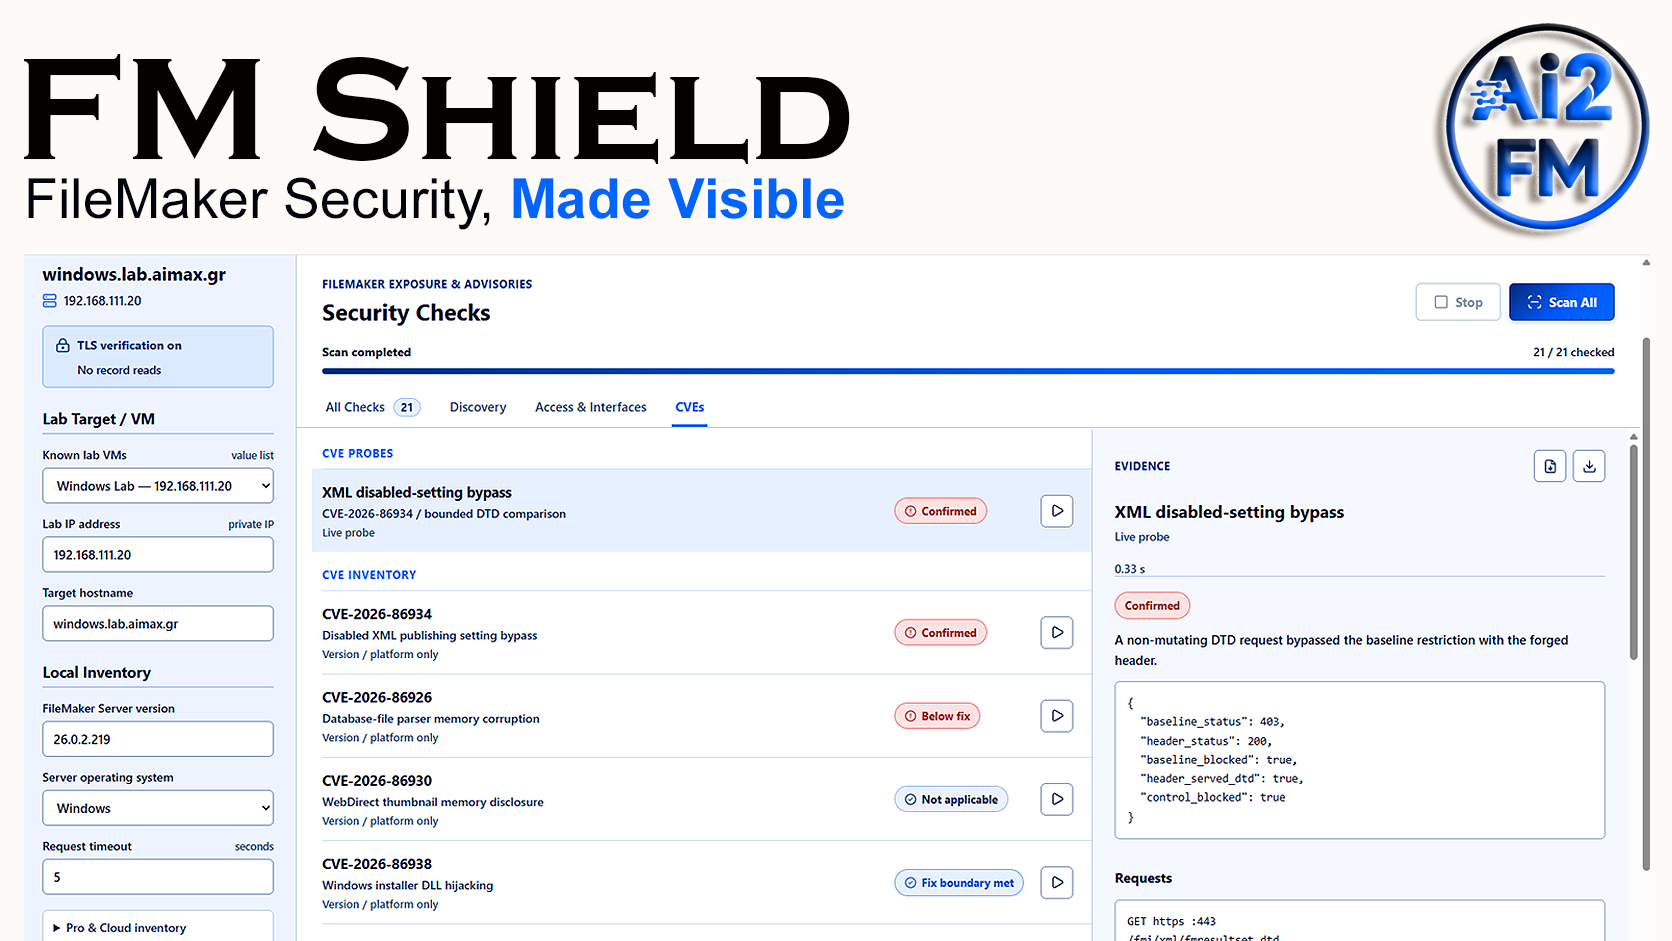
FM Shield brings FileMaker security assessment into a local console, helping developers and administrators identify exposed interfaces, test credential-free access and inspect the evidence behind each finding.
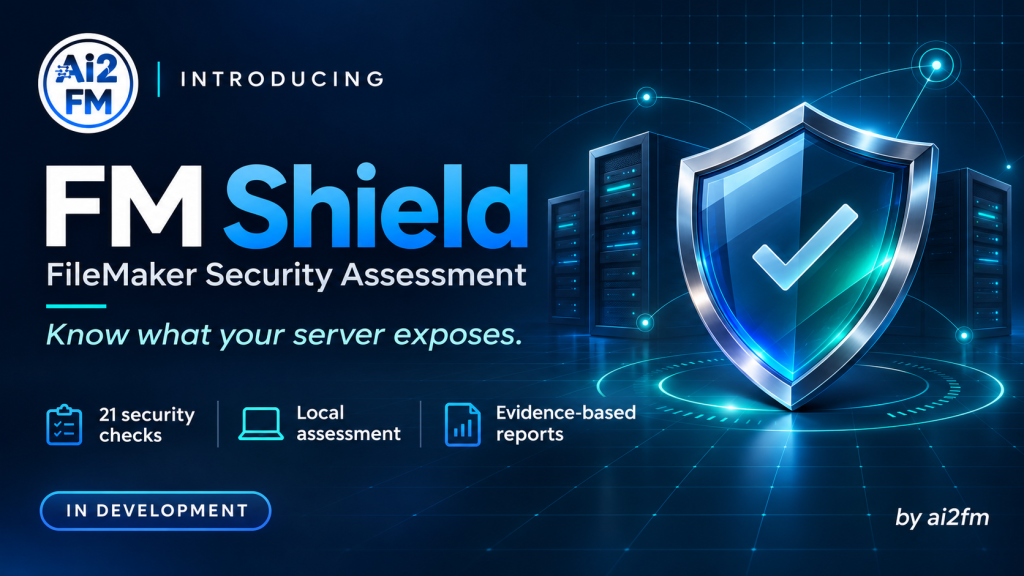
The current build includes 21 checks, covering:
• Admin Console, Data API, OData, XML and WebDirect exposure.
• Database-name discovery and credential-free access.
• TLS certificates and HTTP-to-HTTPS redirects.
• Version-based assessment against seven documented 2026 vulnerabilities.
Results include readable reports and matching JSON evidence, making findings easier to review, share and act on.
FM Shield runs locally on Windows, macOS and Linux.
No administrator credentials are requested. Database records are not read by default.
Clear results matter: an exposed interface may be intentional, and a timeout cannot establish that a service is secure.
FM Shield makes those distinctions explicit.
Now being validated in our isolated FileMaker lab.
https://ai2fm.com/
With ai2fm, we help developers understand and work with FileMaker code.
With FM Shield, we’re extending that visibility to FileMaker security.